

Security Research
Research. Analyze. Secure.
Real-world security research covering DAST, AI-assisted vulnerability analysis, attack chain modeling, and engineering benchmarks.
LATEST RESEARCH
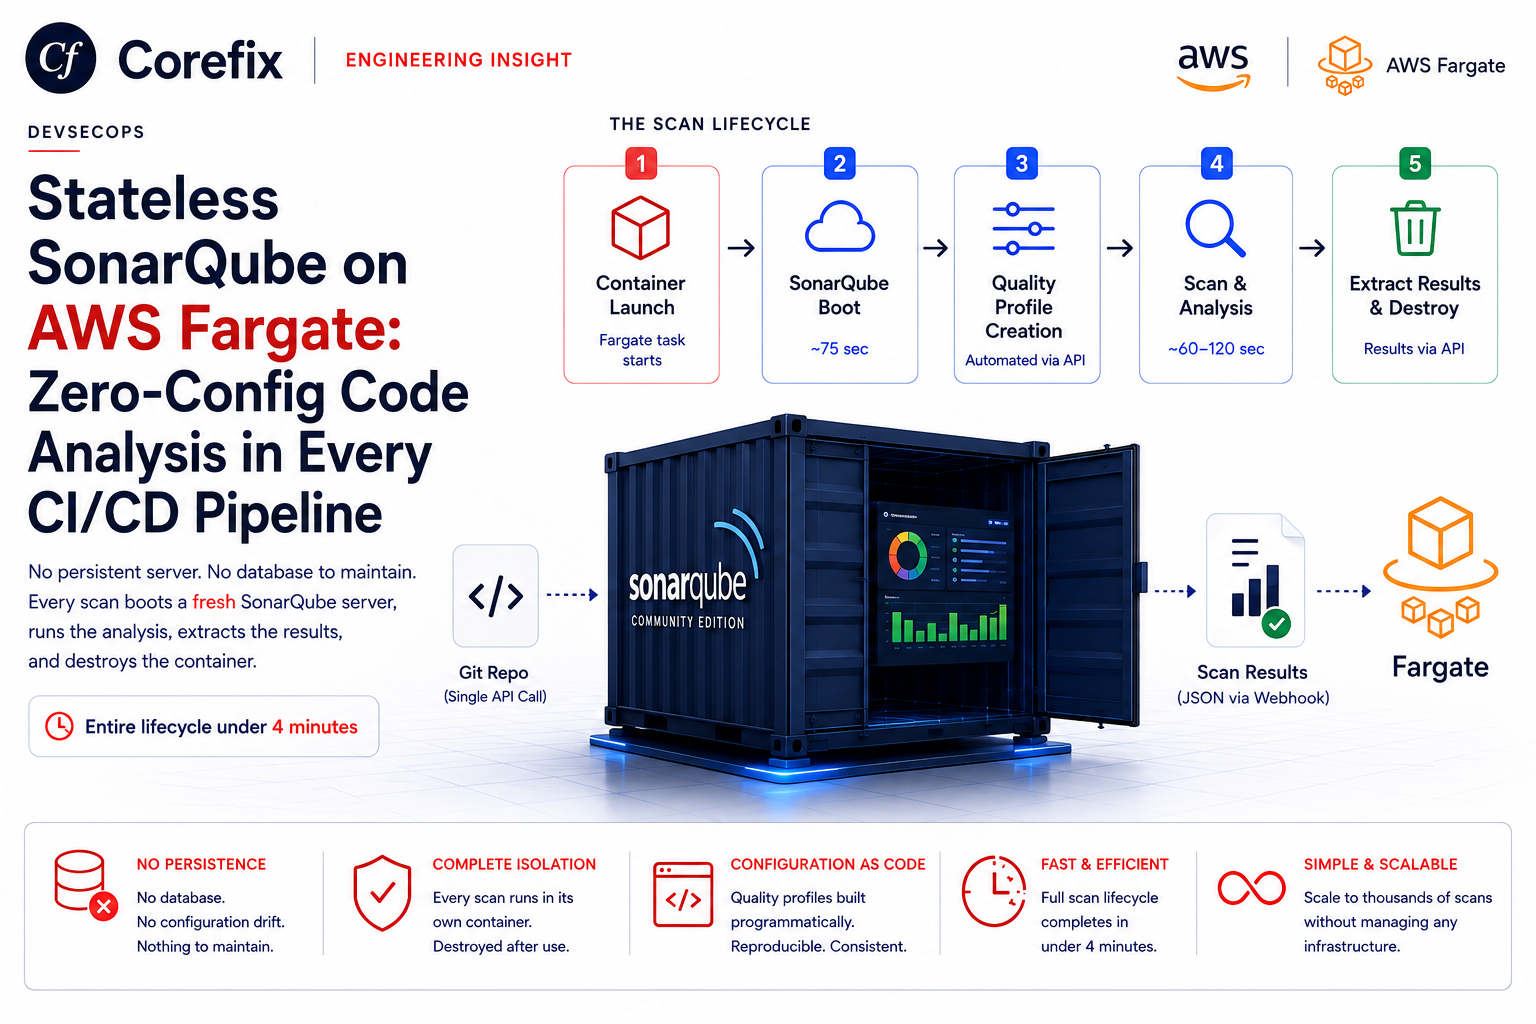
Stateless SonarQube on AWS Fargate: Zero-Config Code Analysis in Every CI/CD Pipeline
No persistent instance, no database, no configuration drift. Every scan boots a fresh SonarQube server on Fargate, runs the analysis, extracts the results, and destroys the container — in under 4 minutes.
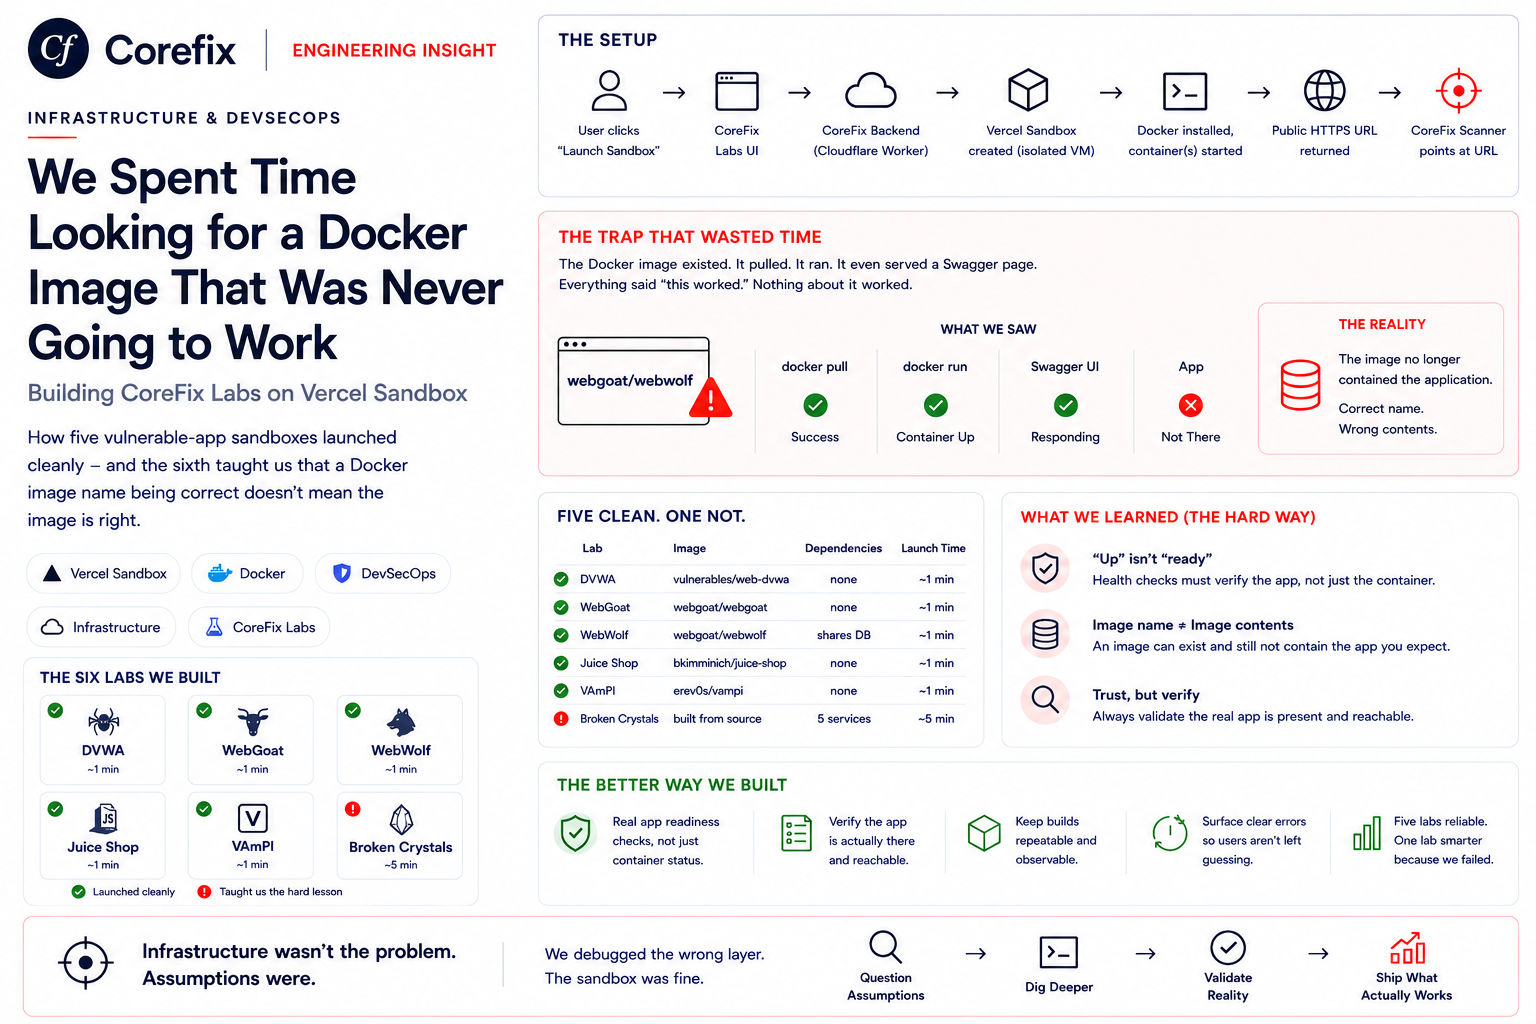
We Spent Days Looking for a Docker Image That Was Never Going to Work: Building CoreFix Labs on Vercel Sandbox
How five vulnerable-app sandboxes launched cleanly - and the sixth taught us that a Docker image name being correct doesn't mean the image is right.
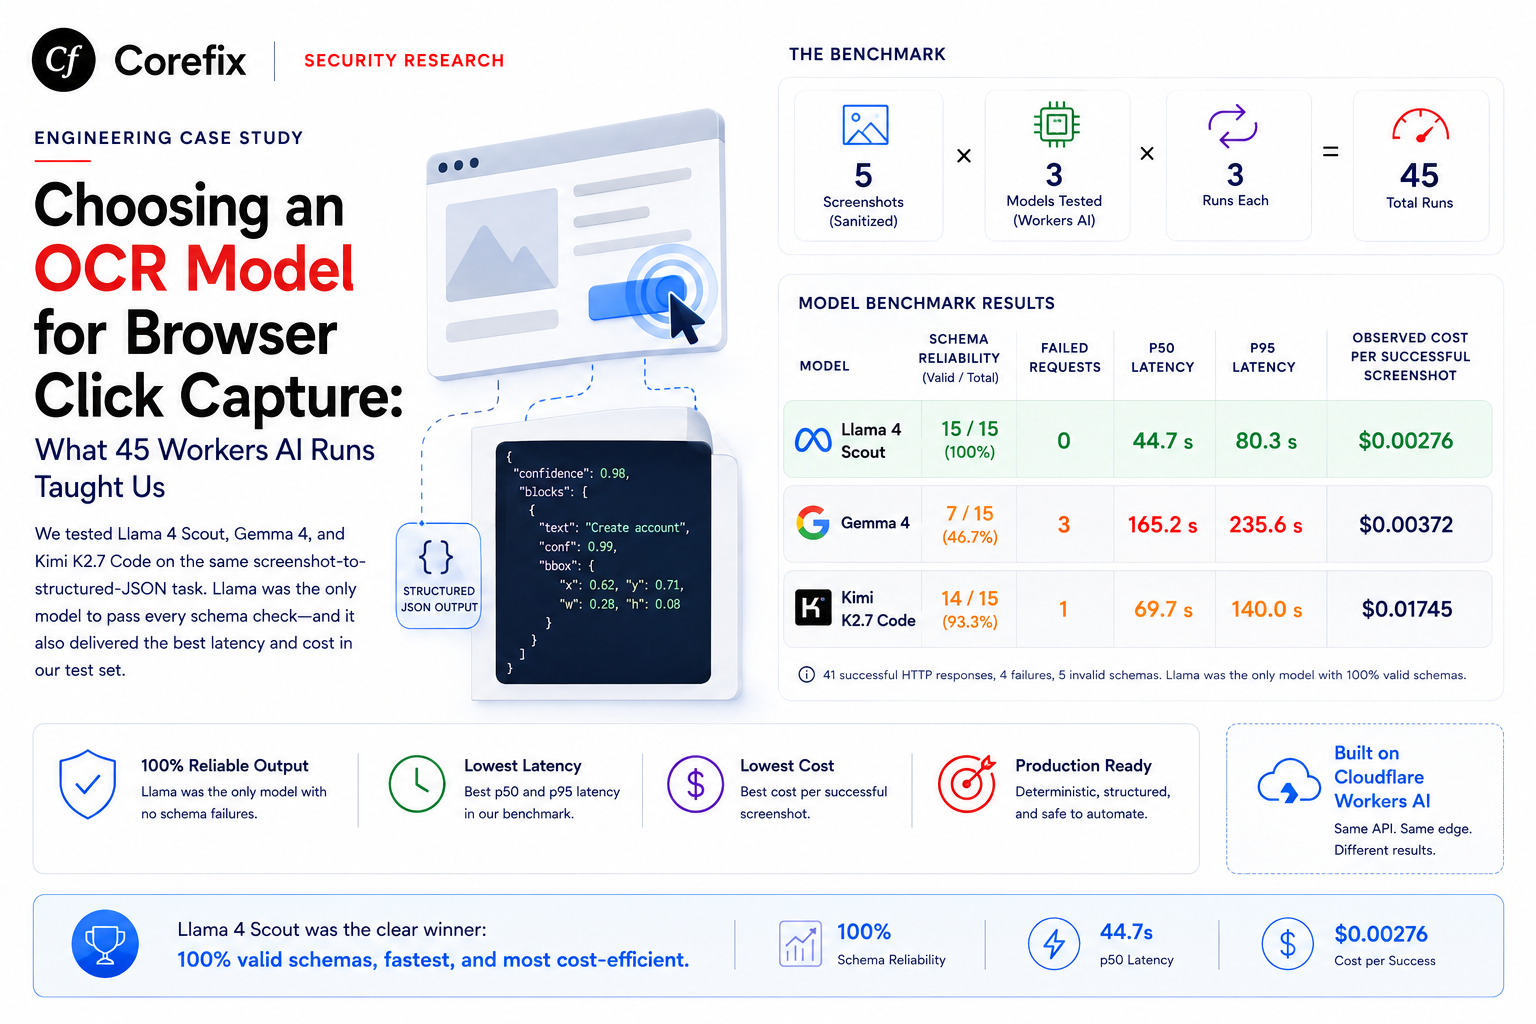
Choosing an OCR Model for Browser Click Capture: What 45 Workers AI Runs Taught Us
We tested Llama 4 Scout, Gemma 4, and Kimi K2.7 Code on the same screenshot-to-structured-JSON task. Llama was the only model to pass every schema check — and it also delivered the best latency and observed cost in our test set.
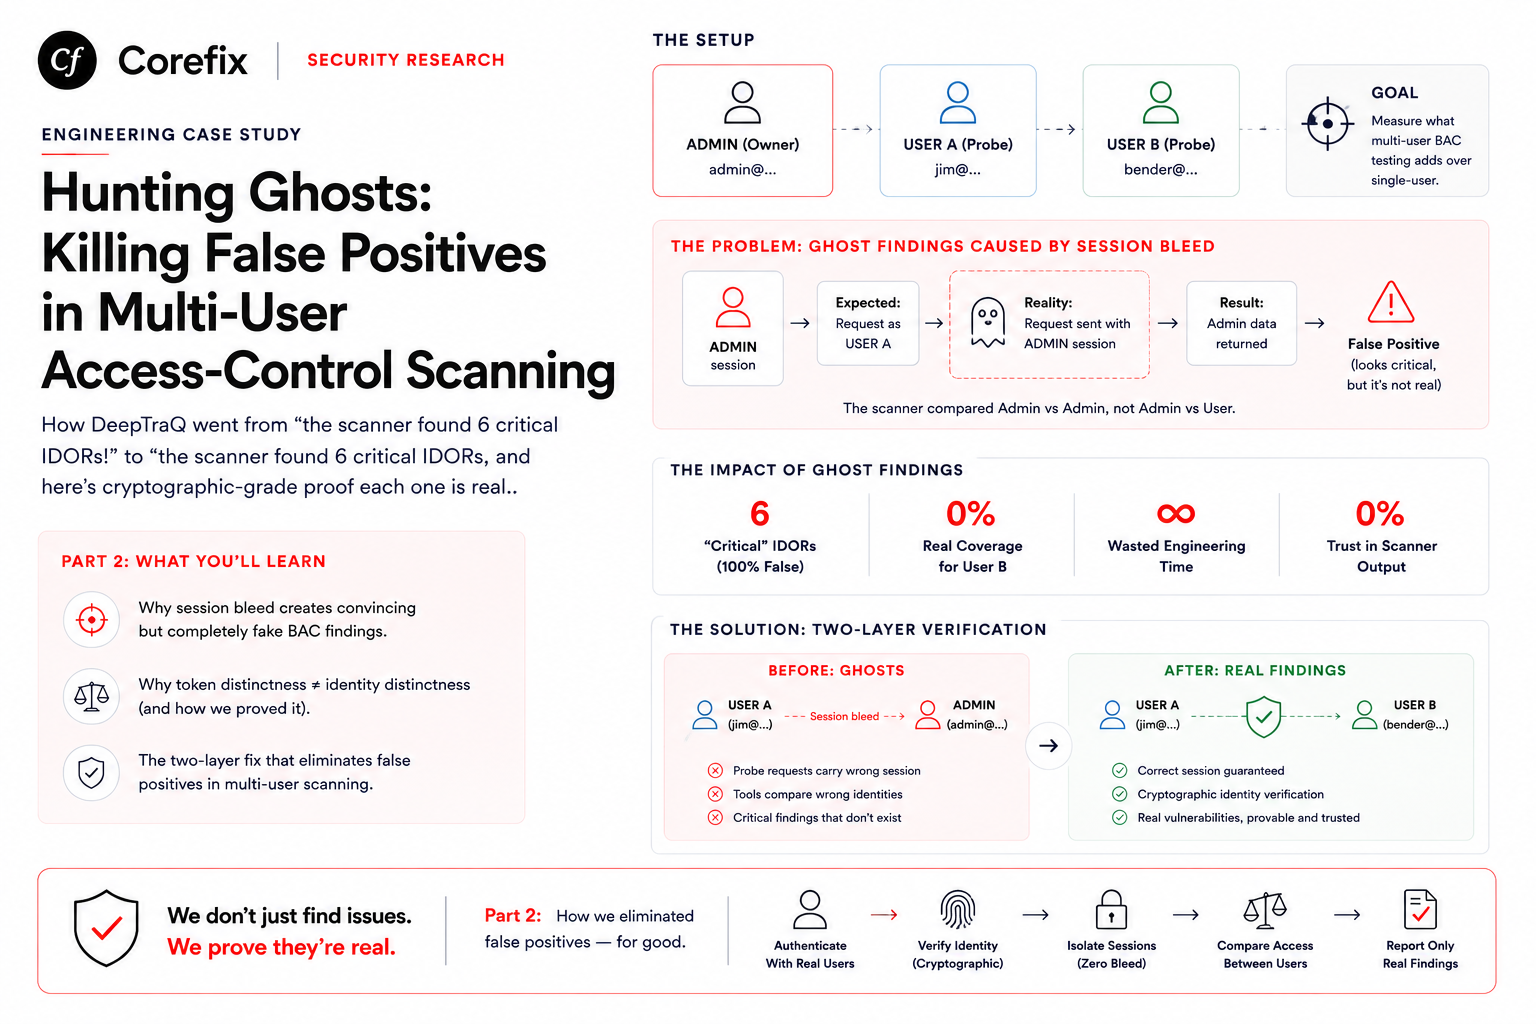
Part 2 — Hunting Ghosts: Killing False Positives in Multi-User Access-Control Scanning
How DeepTraQ went from "the scanner found 6 critical IDORs!" to "the scanner found 6 critical IDORs, and here's cryptographic-grade proof each one is real."
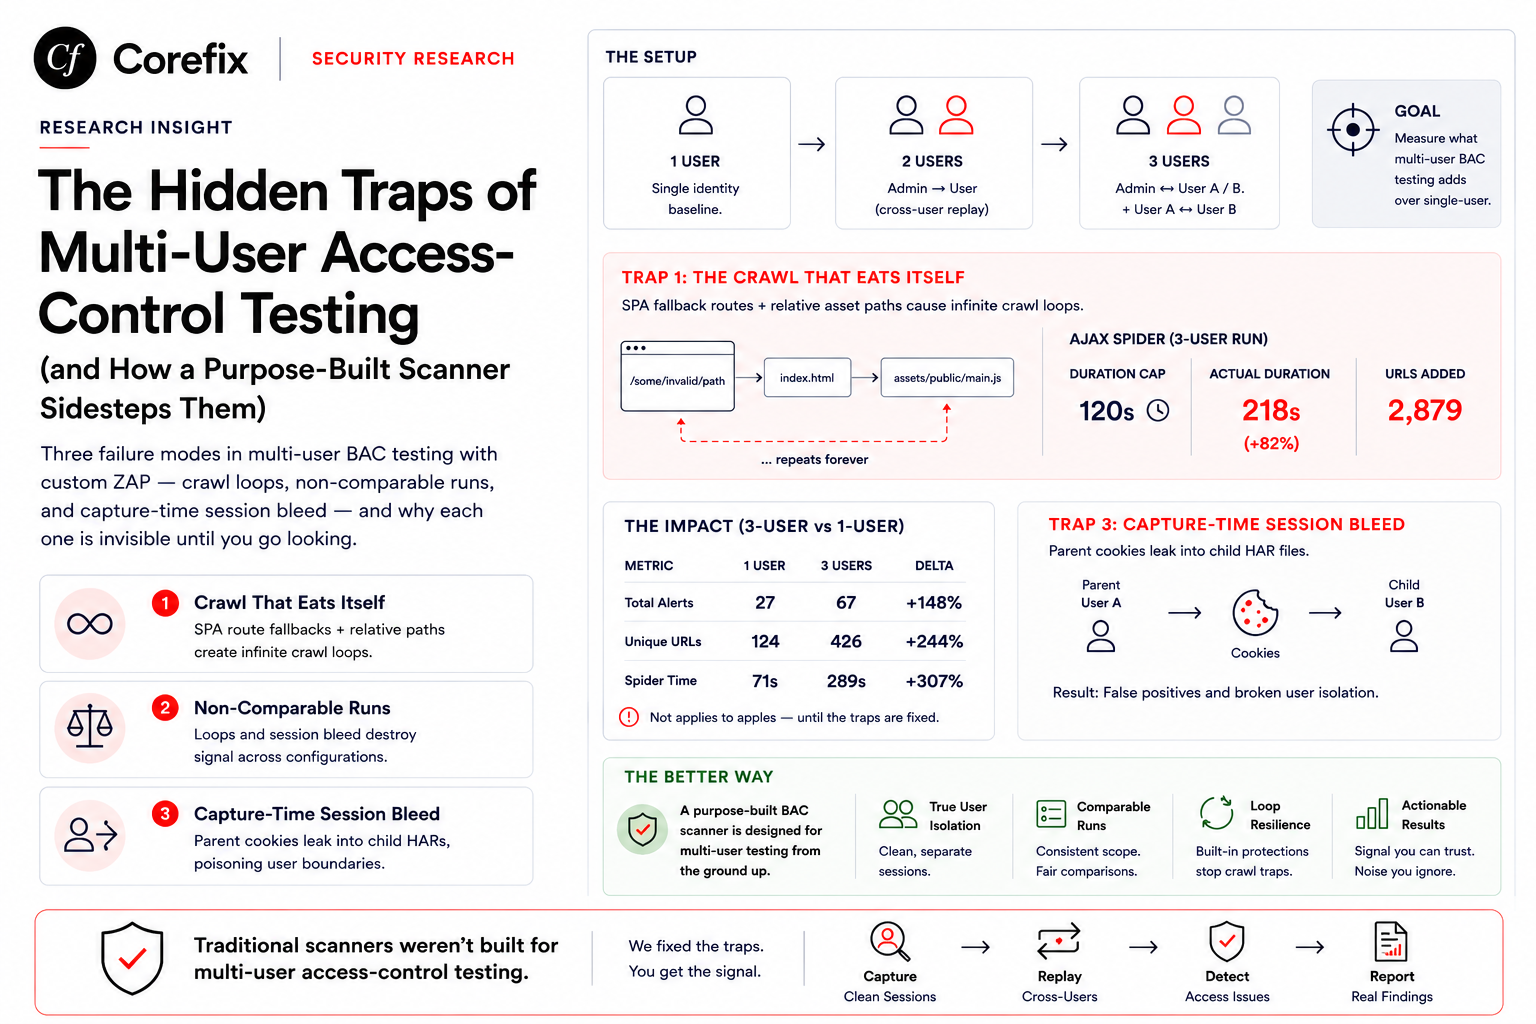
Part 1 — The Hidden Traps of Multi-User Access-Control Testing (and How a Purpose-Built Scanner Sidesteps Them)
Three failure modes in multi-user BAC testing with custom ZAP — crawl loops, non-comparable runs, and capture-time session bleed — and why each one is invisible until you go looking.
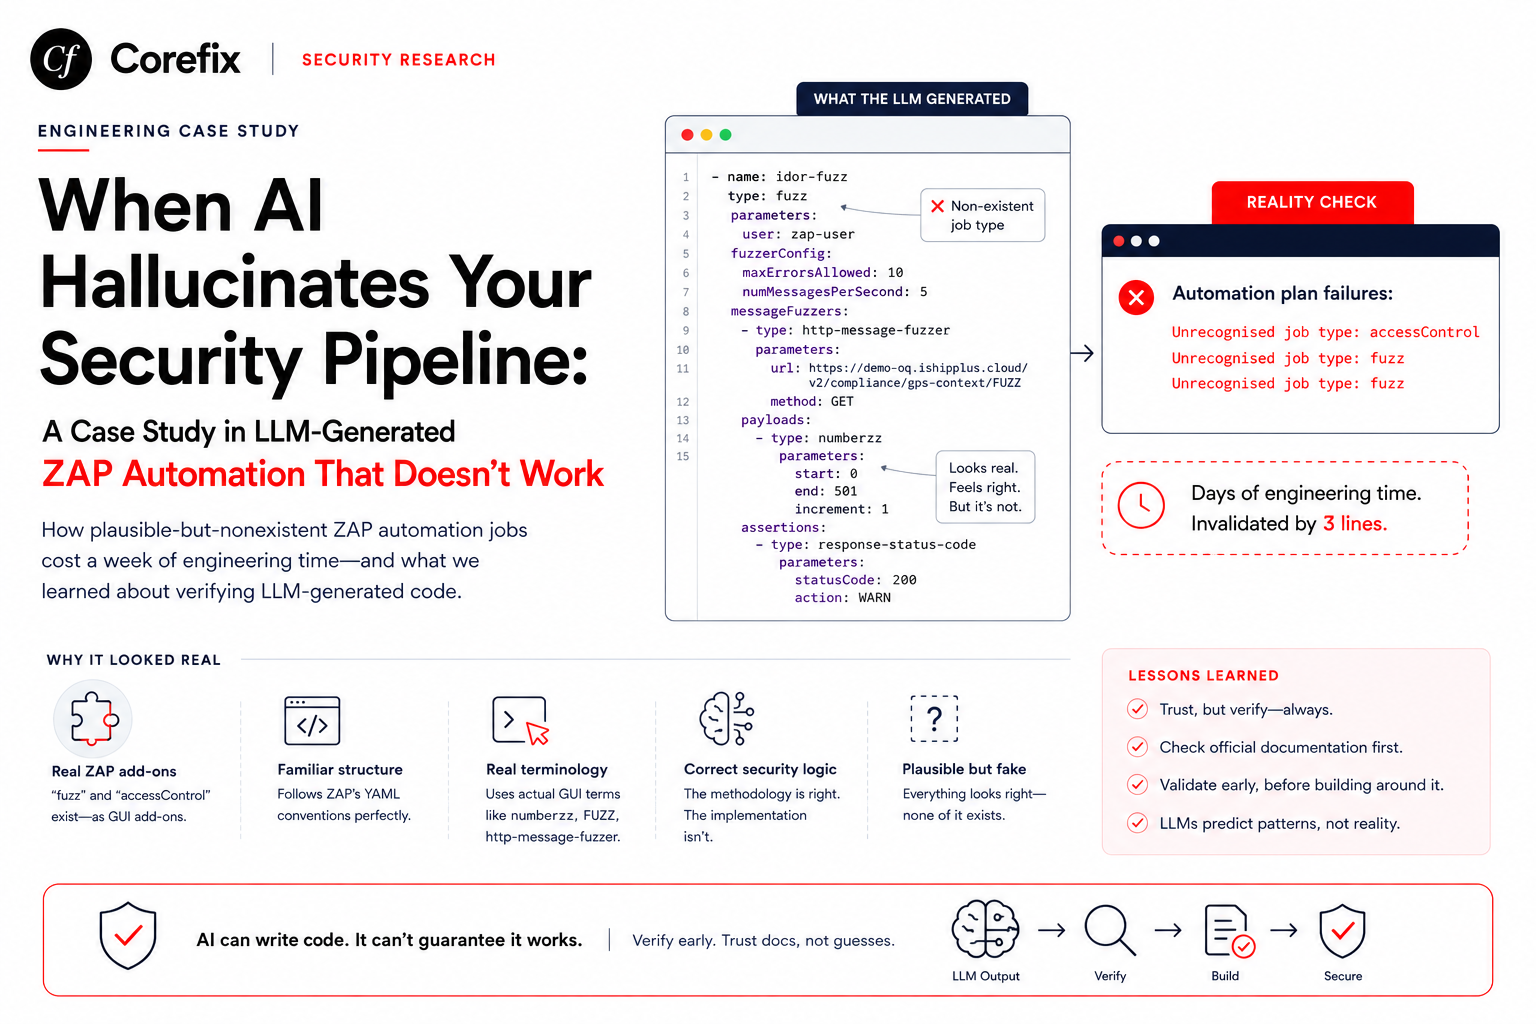
When AI Hallucinates Your Security Pipeline: A Case Study in LLM-Generated ZAP Automation That Doesn't Work
An LLM generated ZAP automation YAML that looked perfect and referenced job types that don't exist. A case study in plausible-but-nonexistent APIs, and what it cost to catch it five days late.
Explore Corefix
Platform
Discover how Corefix helps security teams identify, prioritize, and remediate vulnerabilities across cloud, web, code, and infrastructure environments.
Visit Website →Documentation
Setup guides, scanner integrations, workflows, remediation automation, API references, and complete product documentation.
View Documentation →Roadmap
See upcoming releases, planned features, product improvements, and the future direction of Corefix.
View Roadmap →